tzuctf做题记录Misc
沉睡的密码本
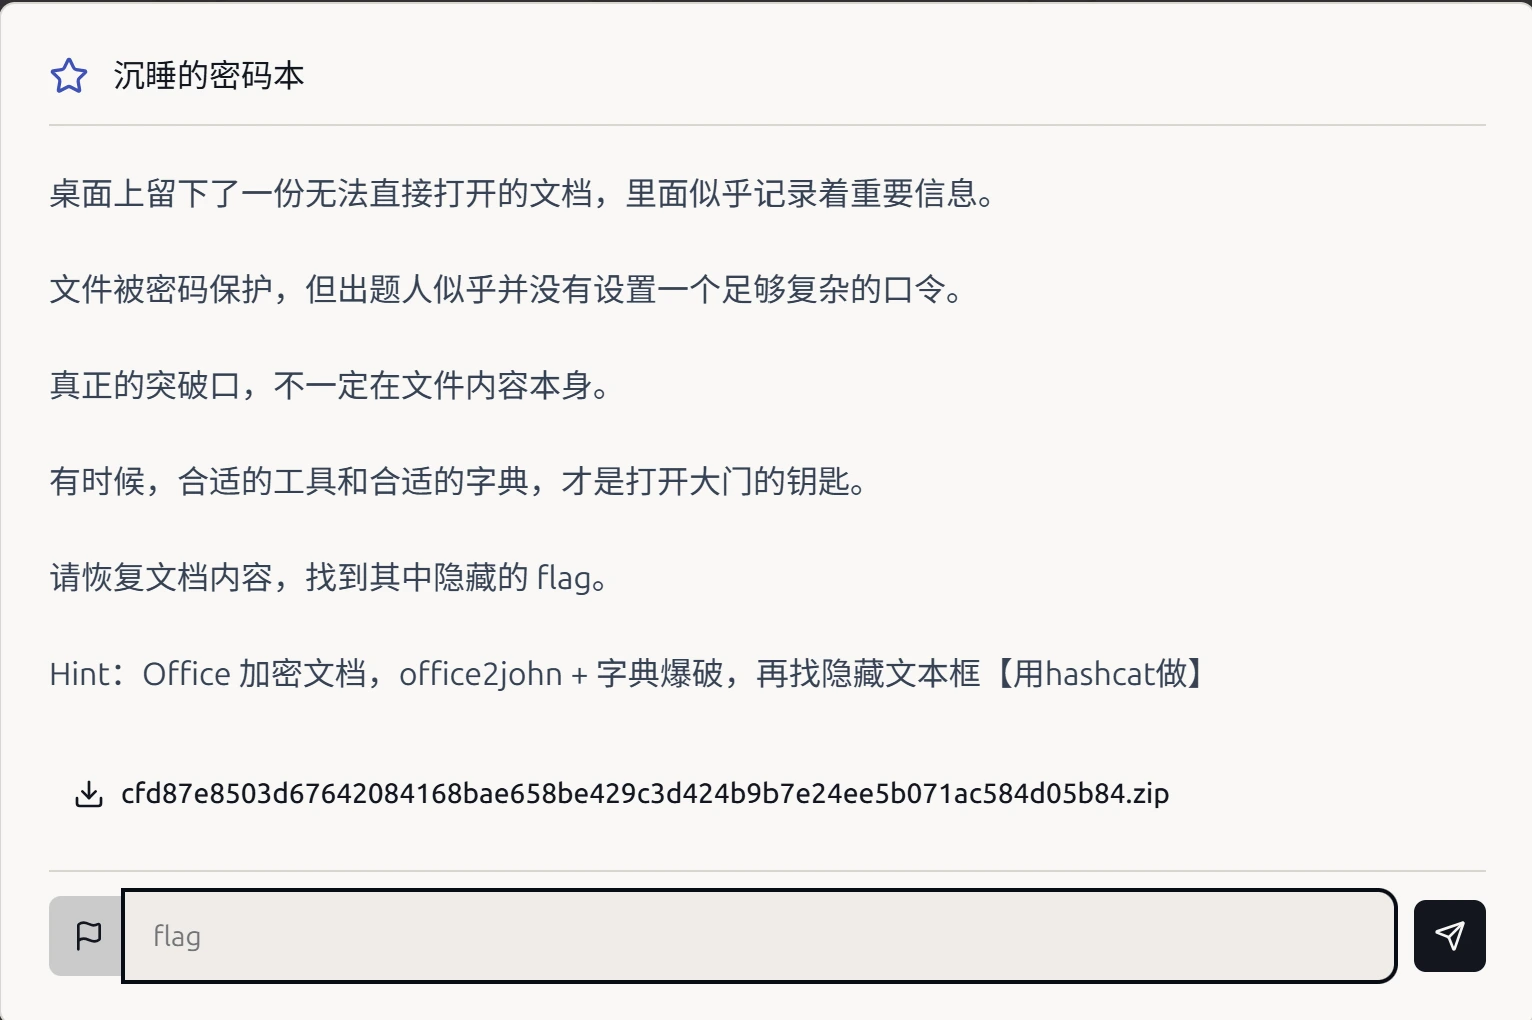 首先先把文件下下来
unzip解压能看到一个叫“What kind of document is this?”的文件,没后缀
然后看看是什么文件类型
1
2
| aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ file "What kind of document is this?"
What kind of document is this?: CDFV2 Encrypted
|
看不懂,问ai
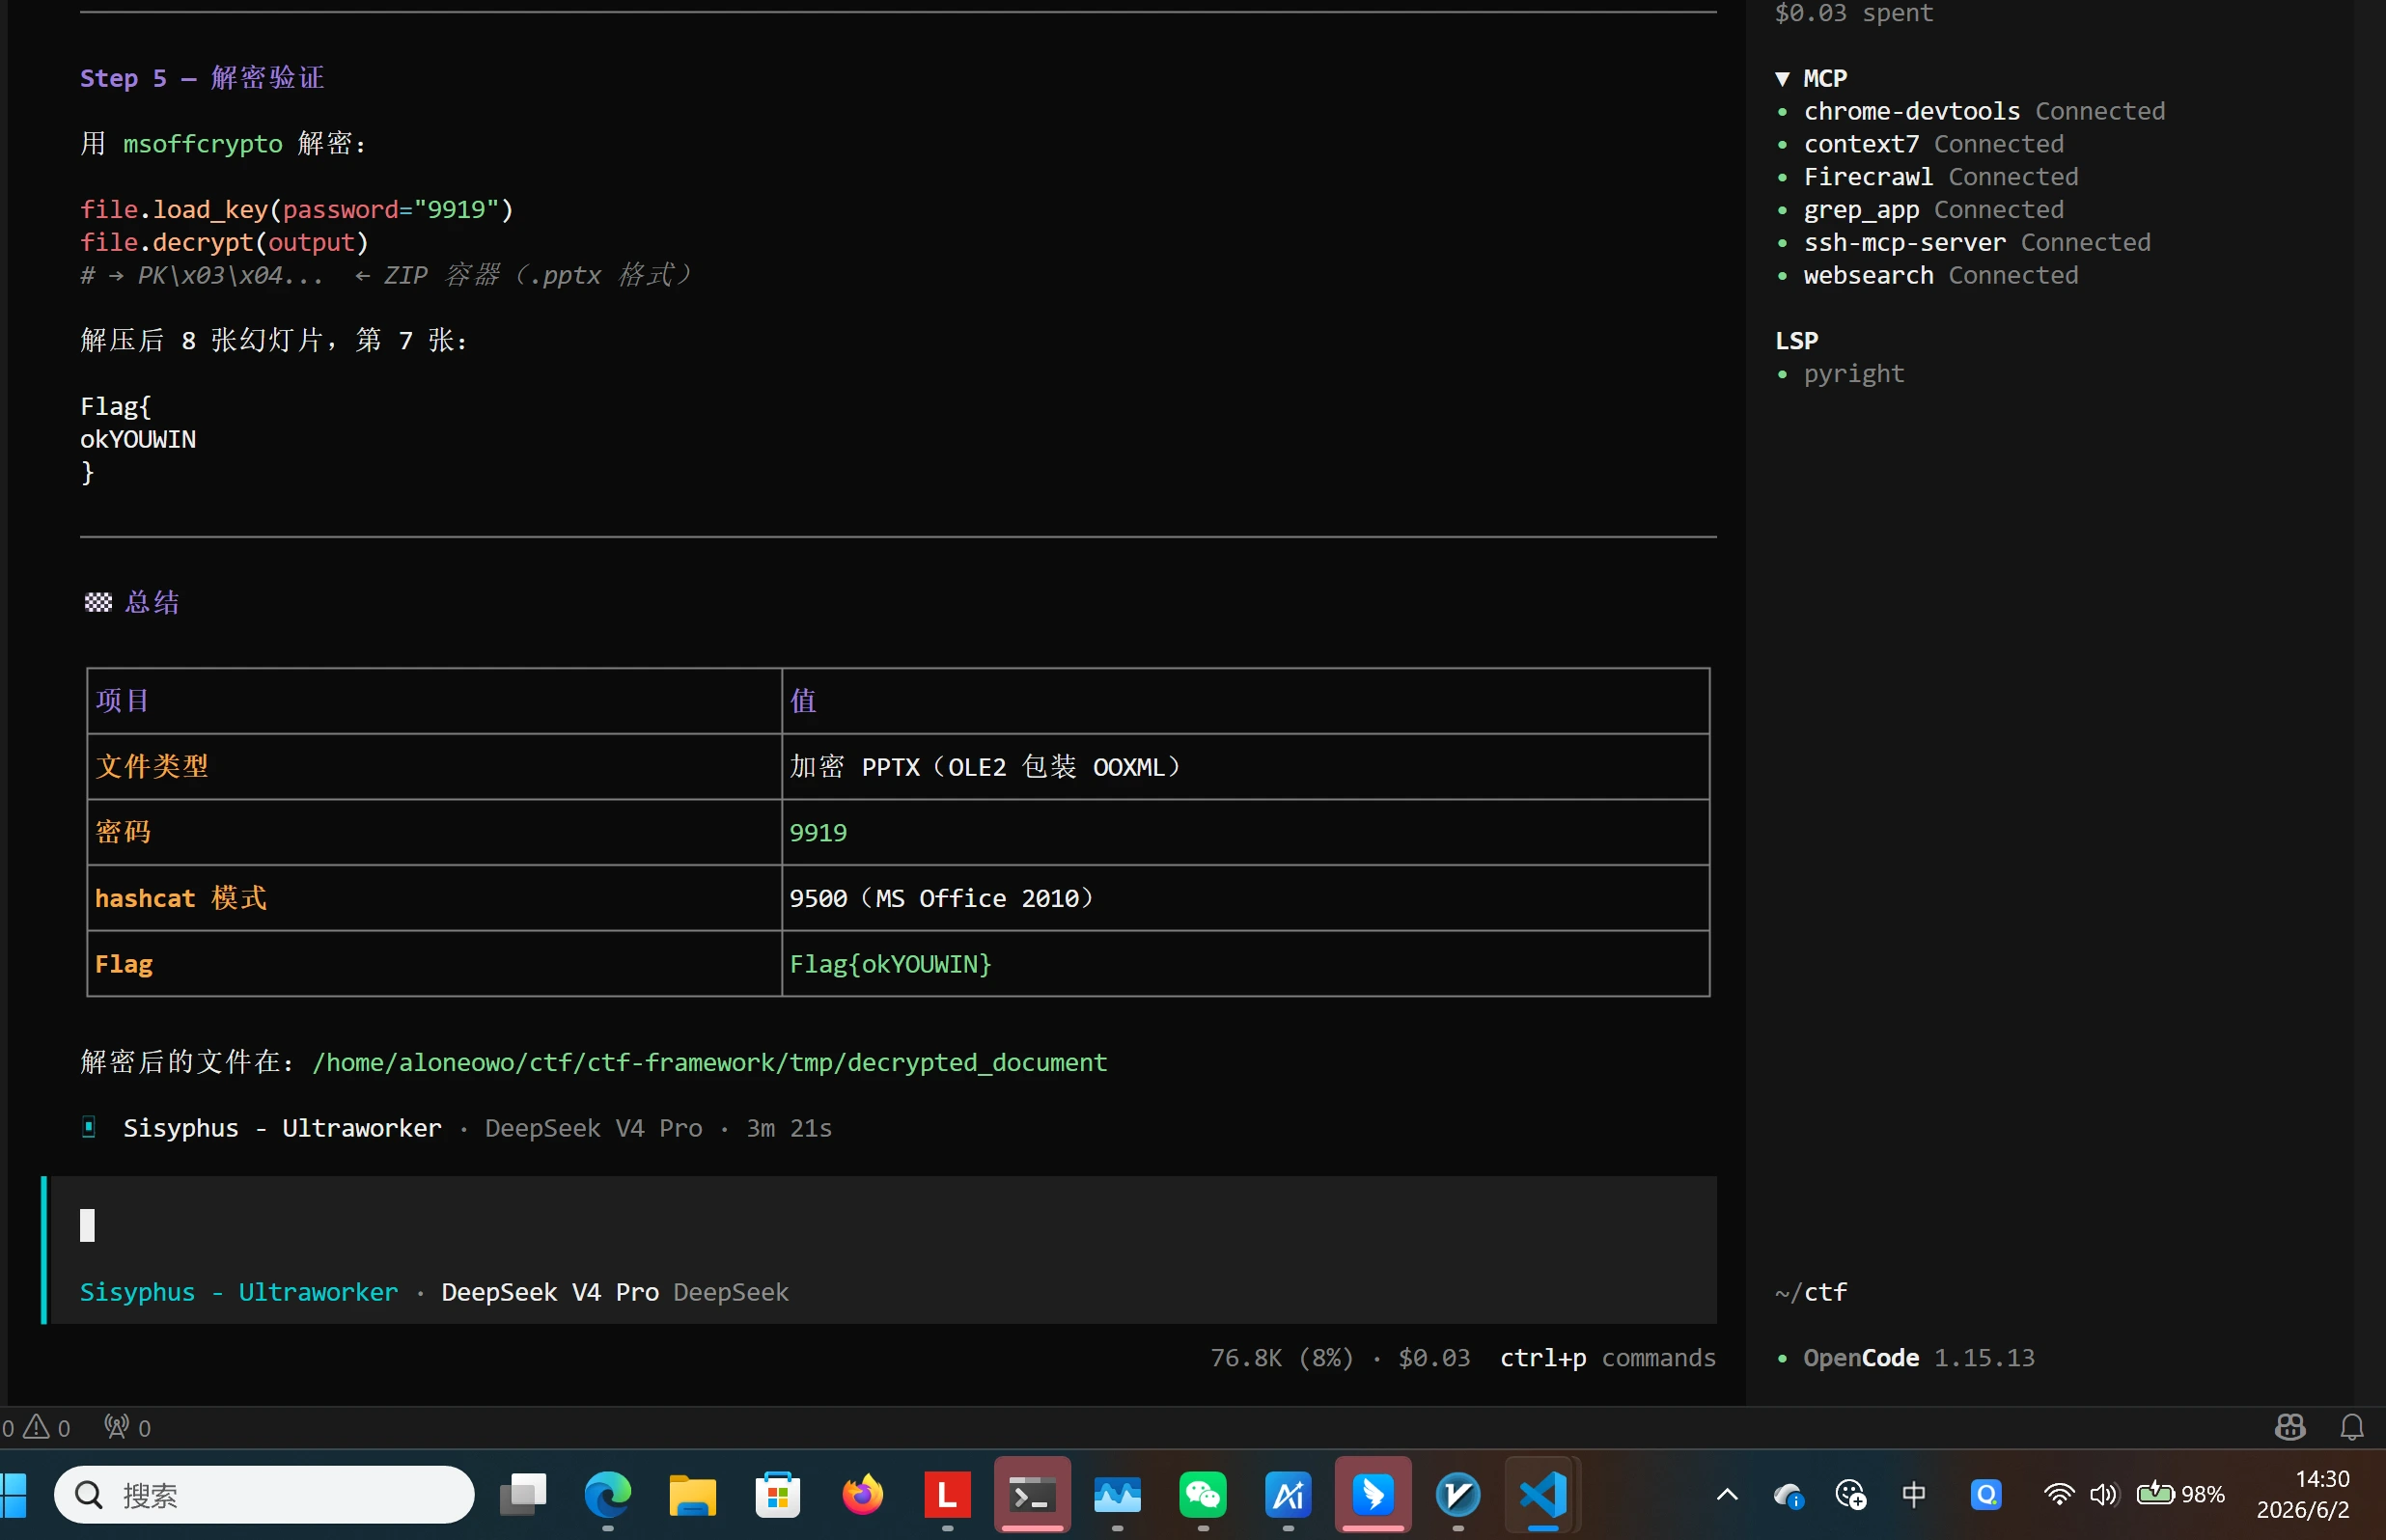
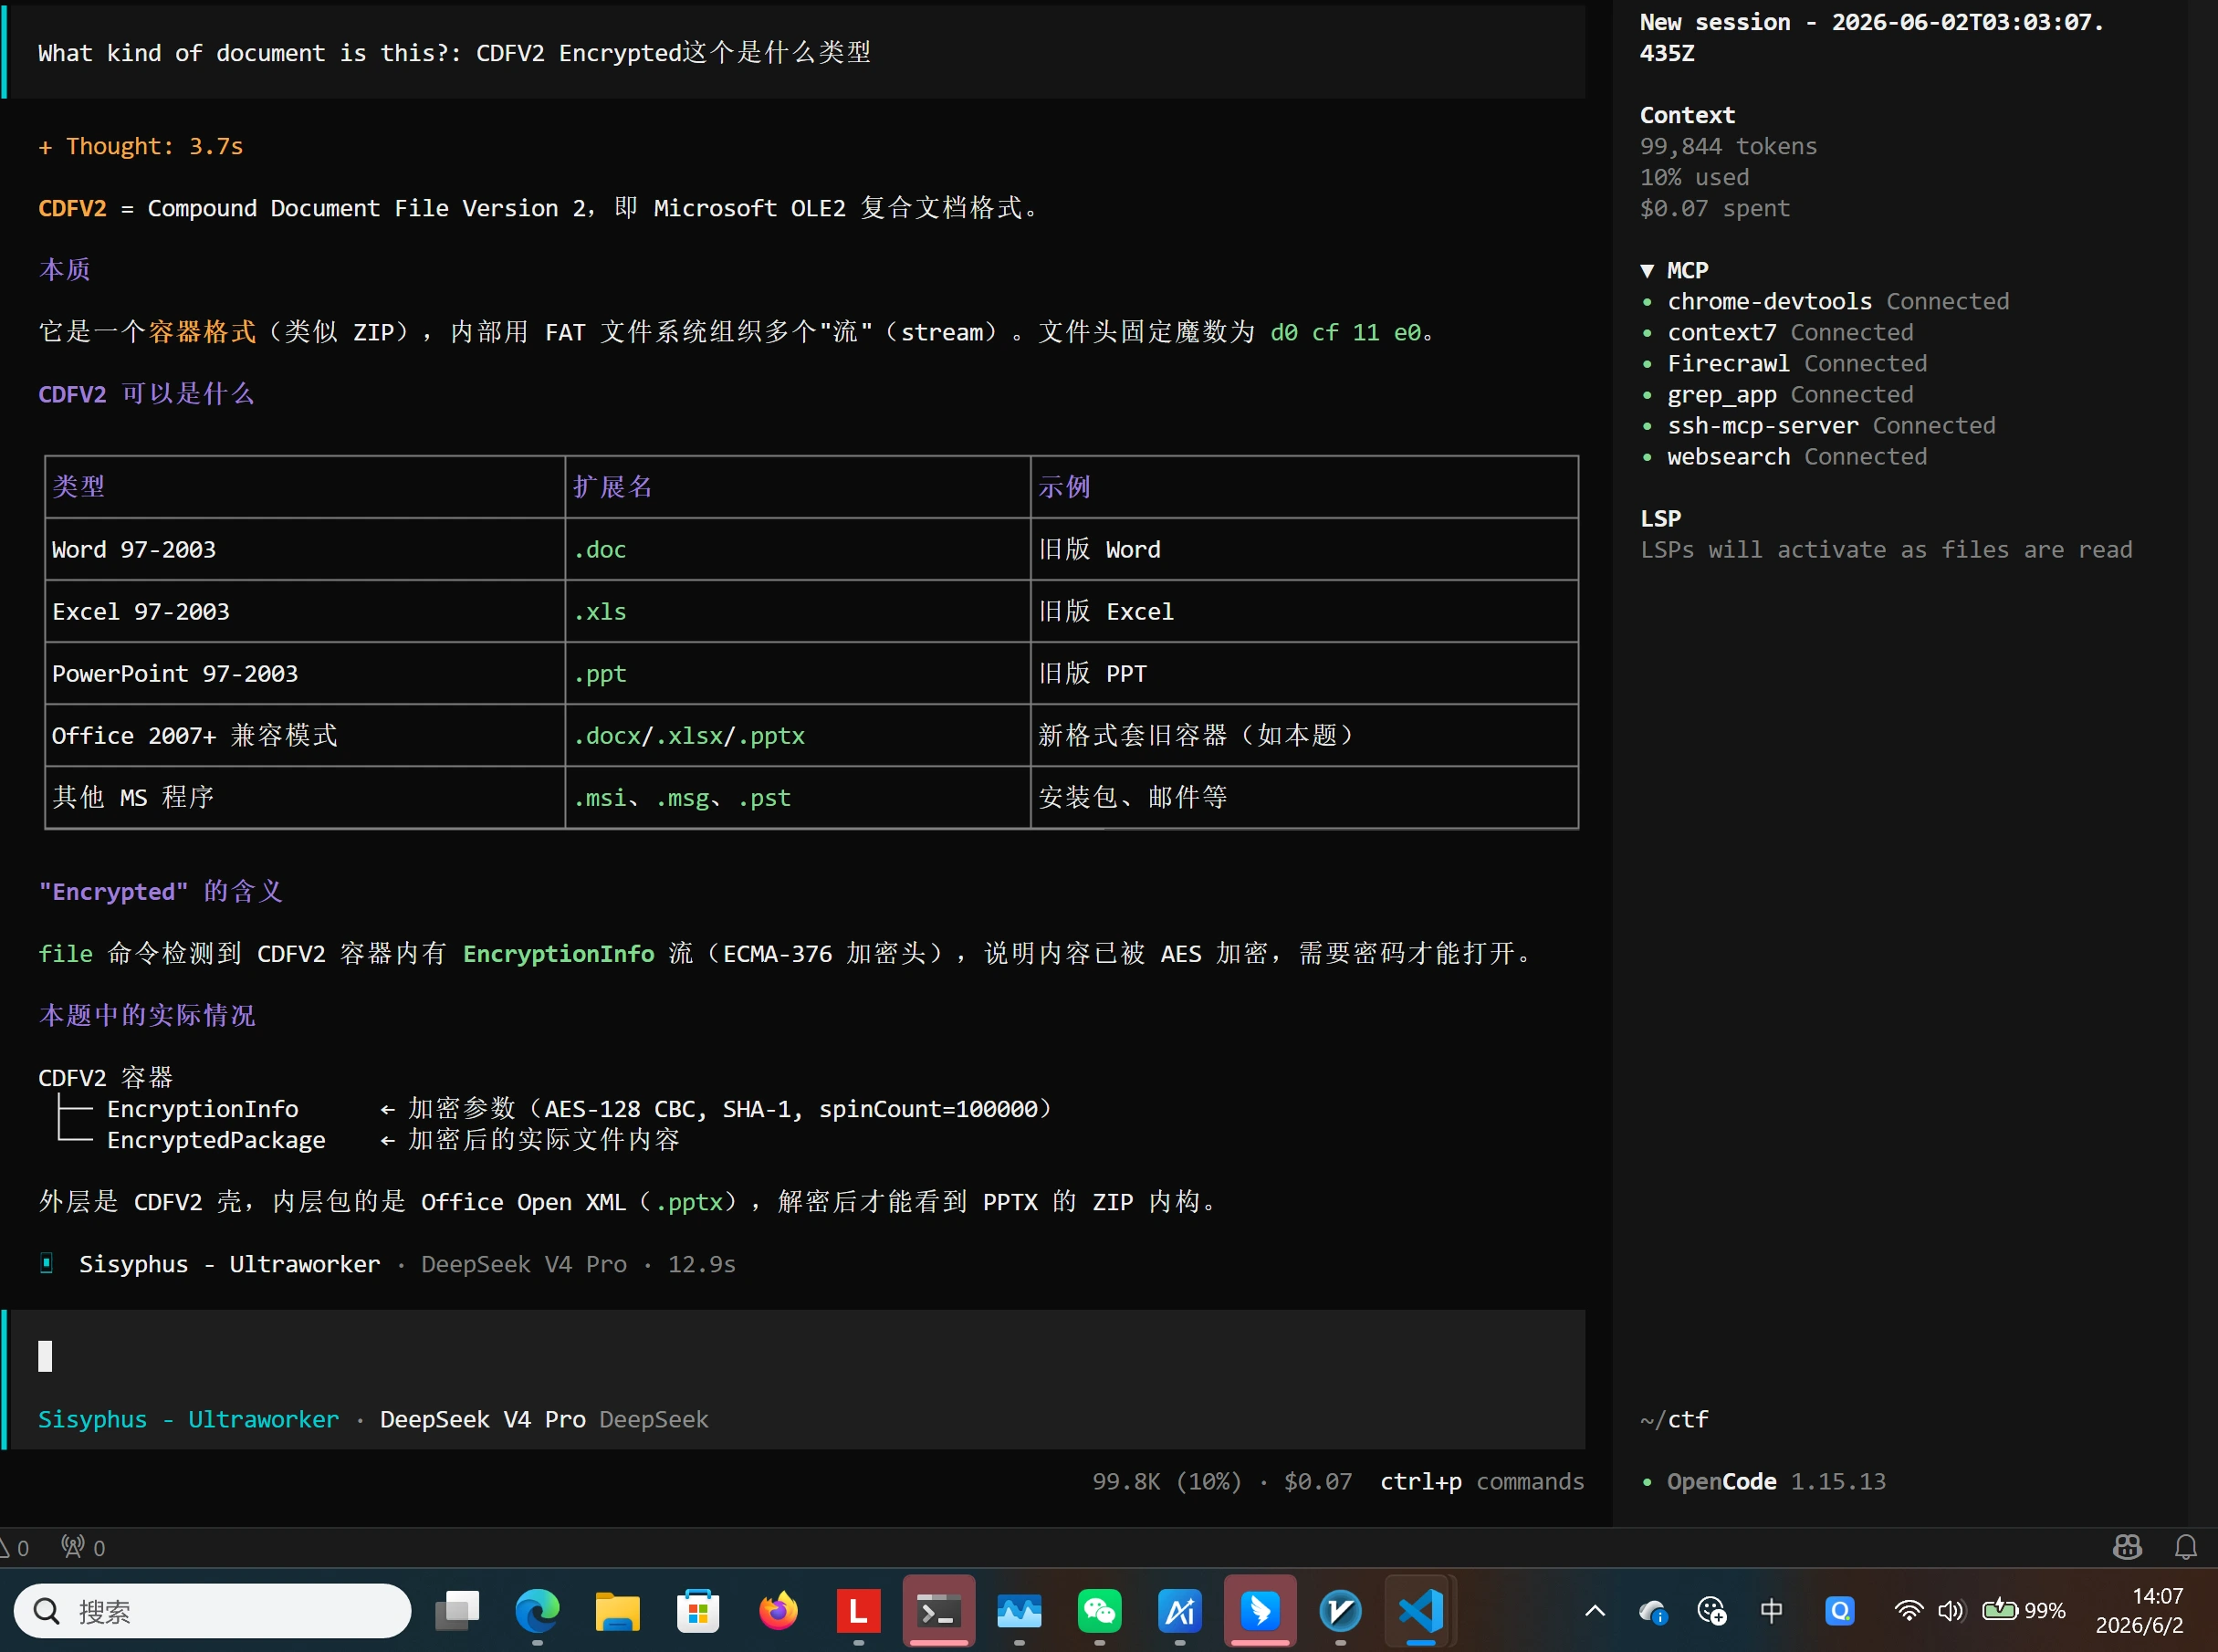 然后尝试让ai用hashcat破解一下这个文件
 问ai这个是什么文件
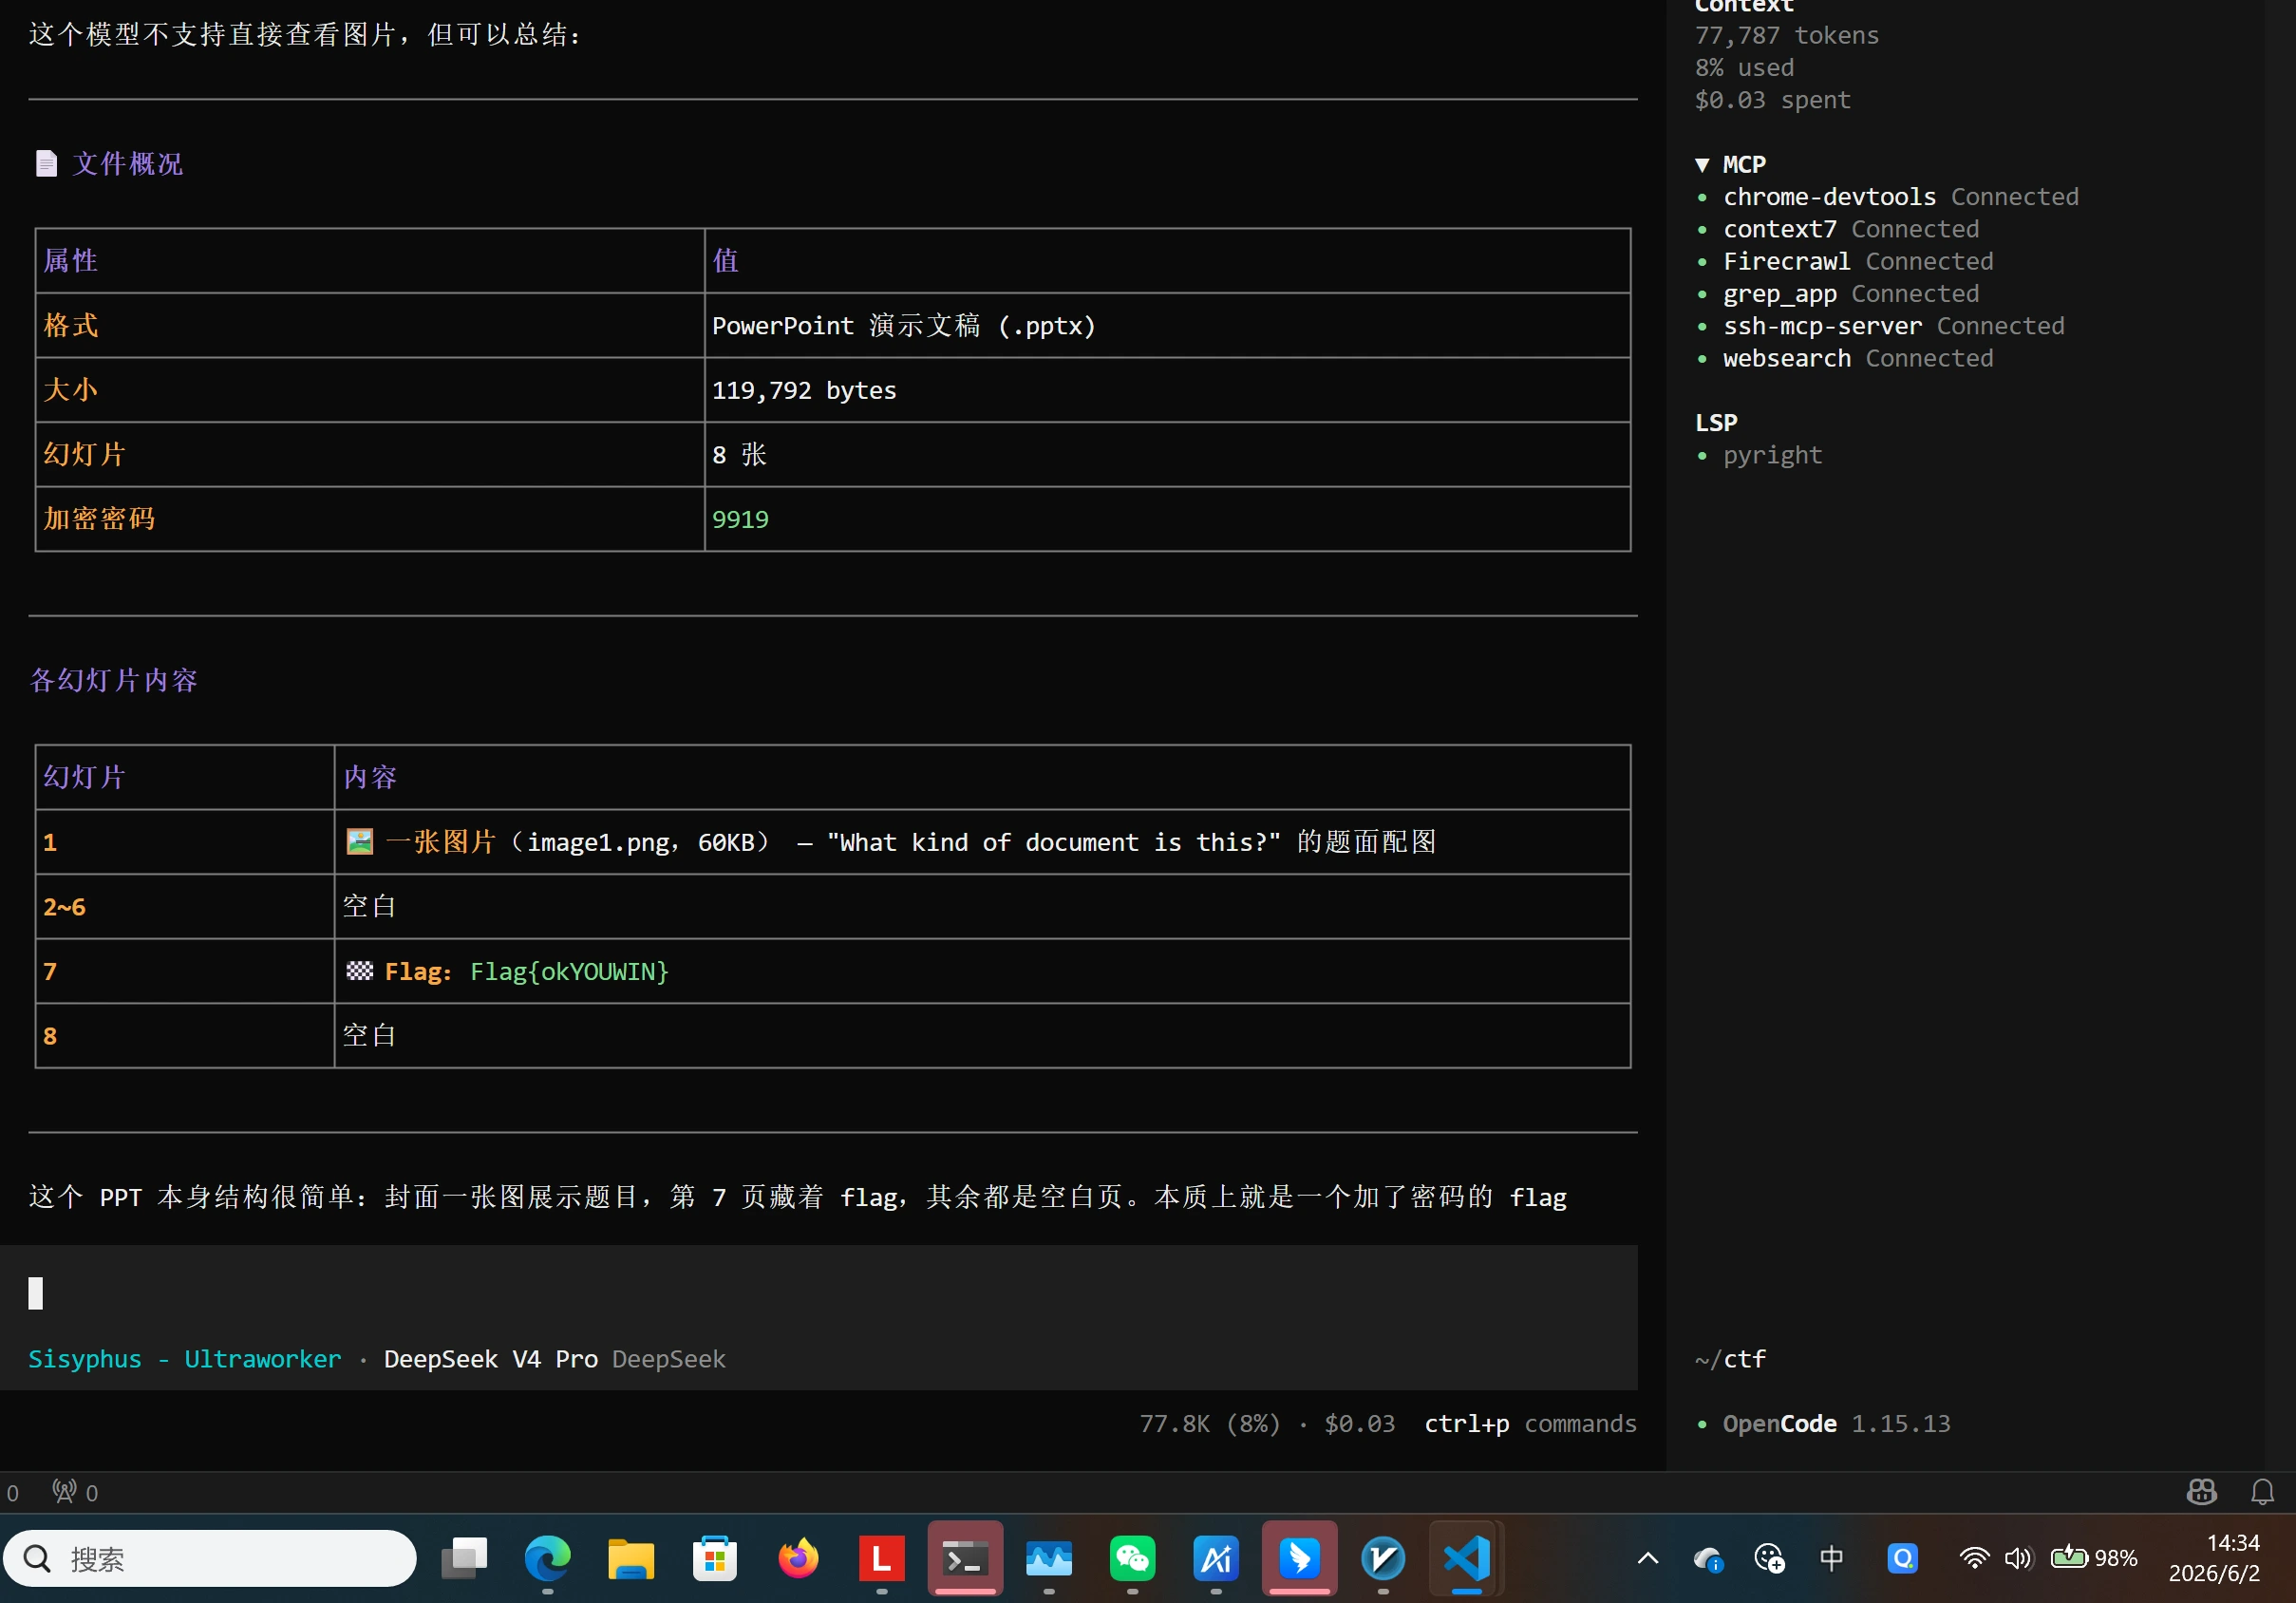 ai直接读取了ppt里面的字符,我打开看了一下
 这种也就骗骗人类了Flag{okYOUWIN}
旧档案的裂缝
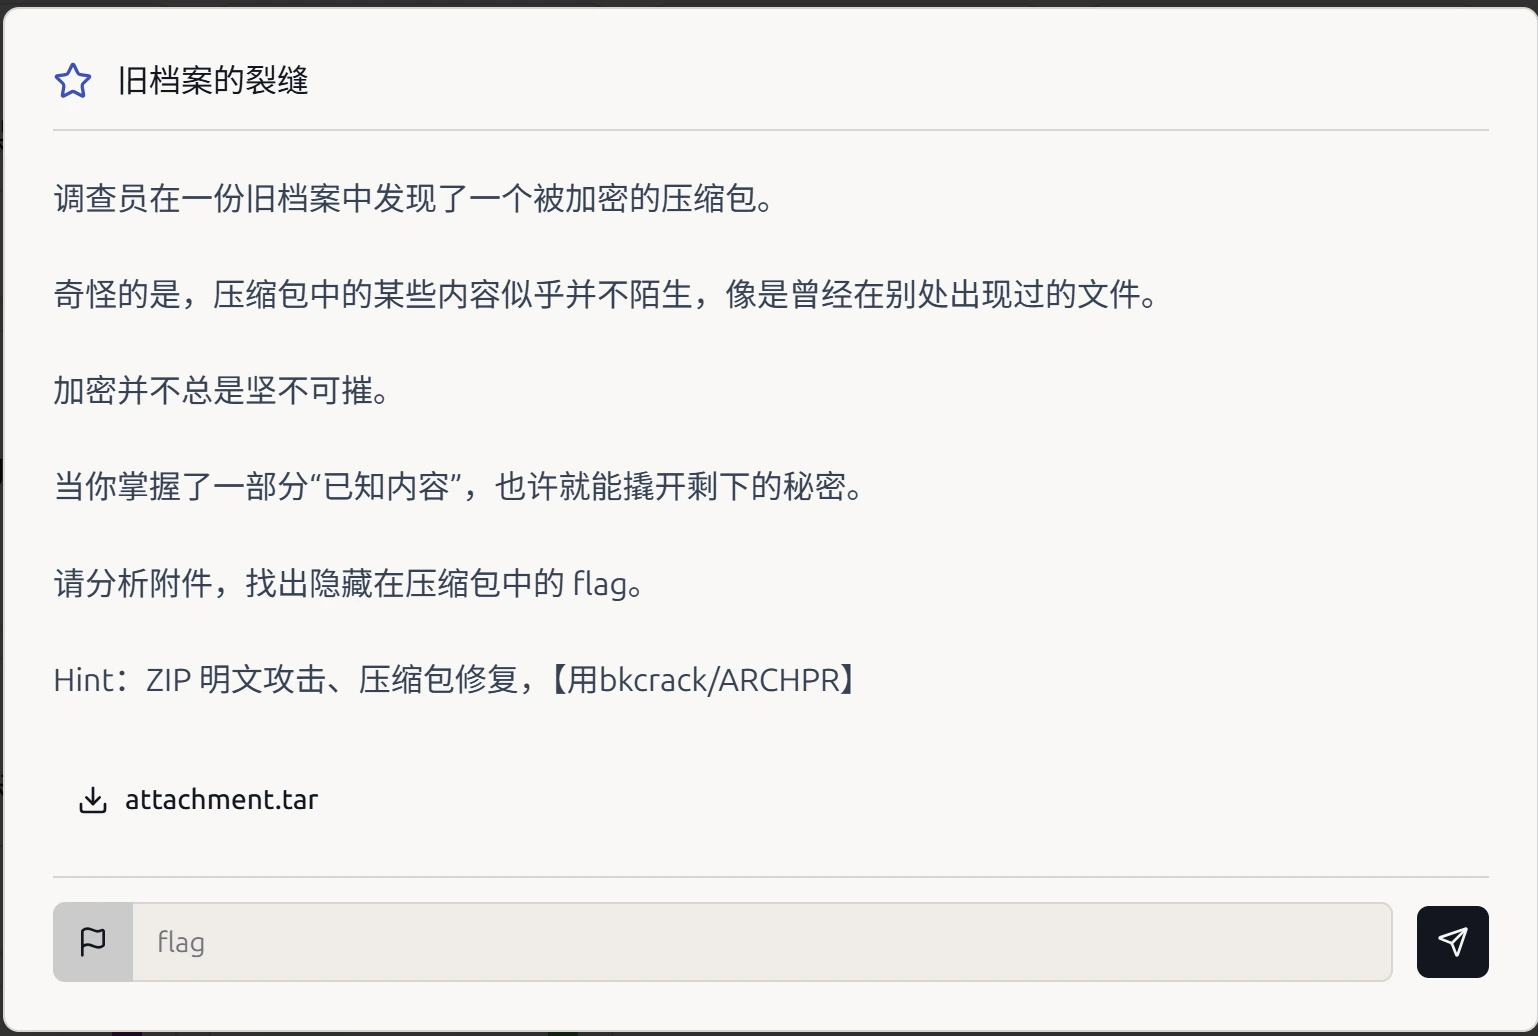
  1
  2
  3
  4
  5
  6
  7
  8
  9
 10
 11
 12
 13
 14
 15
 16
 17
 18
 19
 20
 21
 22
 23
 24
 25
 26
 27
 28
 29
 30
 31
 32
 33
 34
 35
 36
 37
 38
 39
 40
 41
 42
 43
 44
 45
 46
 47
 48
 49
 50
 51
 52
 53
 54
 55
 56
 57
 58
 59
 60
 61
 62
 63
 64
 65
 66
 67
 68
 69
 70
 71
 72
 73
 74
 75
 76
 77
 78
 79
 80
 81
 82
 83
 84
 85
 86
 87
 88
 89
 90
 91
 92
 93
 94
 95
 96
 97
 98
 99
100
101
102
103
104
105
106
107
108
109
110
111
112
113
114
115
116
117
118
119
120
121
122
123
124
125
| aloneowo@THINKBOOK:~/ctf$ cd ctf-framework
aloneowo@THINKBOOK:~/ctf/ctf-framework$ cd tmp
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ ls
'QR Code.png' brute_bunny2.py osint_icon
'What kind of document is this?' cfd87e8503d67642084168bae658be429c3d424b9b7e24ee5b071ac584d05b84.zip prison
"Where's bunny.exe" challenge.jpg user
a12a8997-bd88-4b4f-b7fc-26bef215e7dd.jpg decrypted_document 优质牢房.zip
attachment-10.zip extracted.zip 牢房
attachment.tar lsp-smoke 镜厅中的回响
brute_bunny.py office_hash.txt
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ tar attachment.tar
tar: You may not specify more than one '-Acdtrux', '--delete' or '--test-label' option
Try 'tar --help' or 'tar --usage' for more information.
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ tar -xvf attachment.tar
tmp/
tmp/._none.zip
tmp/none.zip
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ cd tmp
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ ls
none.zip
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ unzip nome.zip
unzip: cannot find or open nome.zip, nome.zip.zip or nome.zip.ZIP.
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ unzip none.zip
Archive: none.zip
inflating: res.zip
inflating: woo.jpg
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ unzip res.zip
Archive: res.zip
[res.zip] flag.txt password: aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ zipinfo -v res.zip
Archive: res.zip
There is no zipfile comment.
End-of-central-directory record:
-------------------------------
Zip archive file size: 344 (0000000000000158h)
Actual end-cent-dir record offset: 322 (0000000000000142h)
Expected end-cent-dir record offset: 322 (0000000000000142h)
(based on the length of the central directory and its expected offset)
This zipfile constitutes the sole disk of a single-part archive; its
central directory contains 2 entries.
The central directory is 182 (00000000000000B6h) bytes long,
and its (expected) offset in bytes from the beginning of the zipfile
is 140 (000000000000008Ch).
Central directory entry #1:
---------------------------
flag.txt
offset of local header from start of archive: 0
(0000000000000000h) bytes
file system or operating system of origin: MS-DOS, OS/2 or NT FAT
version of encoding software: 2.0
minimum file system compatibility required: MS-DOS, OS/2 or NT FAT
minimum software version required to extract: 2.0
compression method: deflated
compression sub-type (deflation): normal
file security status: encrypted
extended local header: yes
file last modified on (DOS date/time): 2019 Dec 2 20:22:22
32-bit CRC value (hex): b0c530d8
compressed size: 29 bytes
uncompressed size: 17 bytes
length of filename: 8 characters
length of extra field: 36 bytes
length of file comment: 0 characters
disk number on which file begins: disk 1
apparent file type: binary
non-MSDOS external file attributes: 000000 hex
MS-DOS file attributes (20 hex): arc
The central-directory extra field contains:
- A subfield with ID 0x000a (PKWARE Win32) and 32 data bytes. The first
20 are: 00 00 00 00 01 00 18 00 01 02 2b 25 0b a9 d5 01 92 26 14 c9.
There is no file comment.
Central directory entry #2:
---------------------------
There are an extra -36 bytes preceding this file.
secret.txt
offset of local header from start of archive: 67
(0000000000000043h) bytes
file system or operating system of origin: MS-DOS, OS/2 or NT FAT
version of encoding software: 2.0
minimum file system compatibility required: MS-DOS, OS/2 or NT FAT
minimum software version required to extract: 2.0
compression method: deflated
compression sub-type (deflation): normal
file security status: encrypted
extended local header: yes
file last modified on (DOS date/time): 2020 Jan 14 13:14:32
32-bit CRC value (hex): 483344c3
compressed size: 33 bytes
uncompressed size: 19 bytes
length of filename: 10 characters
length of extra field: 36 bytes
length of file comment: 0 characters
disk number on which file begins: disk 1
apparent file type: binary
non-MSDOS external file attributes: 000000 hex
MS-DOS file attributes (20 hex): arc
The central-directory extra field contains:
- A subfield with ID 0x000a (PKWARE Win32) and 32 data bytes. The first
20 are: 00 00 00 00 01 00 18 00 a8 7a d6 80 99 ca d5 01 a8 7a d6 80.
There is no file comment.
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$ unzip ._none.zip
Archive: ._none.zip
End-of-central-directory signature not found. Either this file is not
a zipfile, or it constitutes one disk of a multi-part archive. In the
latter case the central directory and zipfile comment will be found on
the last disk(s) of this archive.
unzip: cannot find zipfile directory in one of ._none.zip or
._none.zip.zip, and cannot find ._none.zip.ZIP, period.
aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp/tmp$
|
通过多次解压和获取zipinfo可以看到,reszip里面有一个flag。
让ai分析一下这些文件的异常
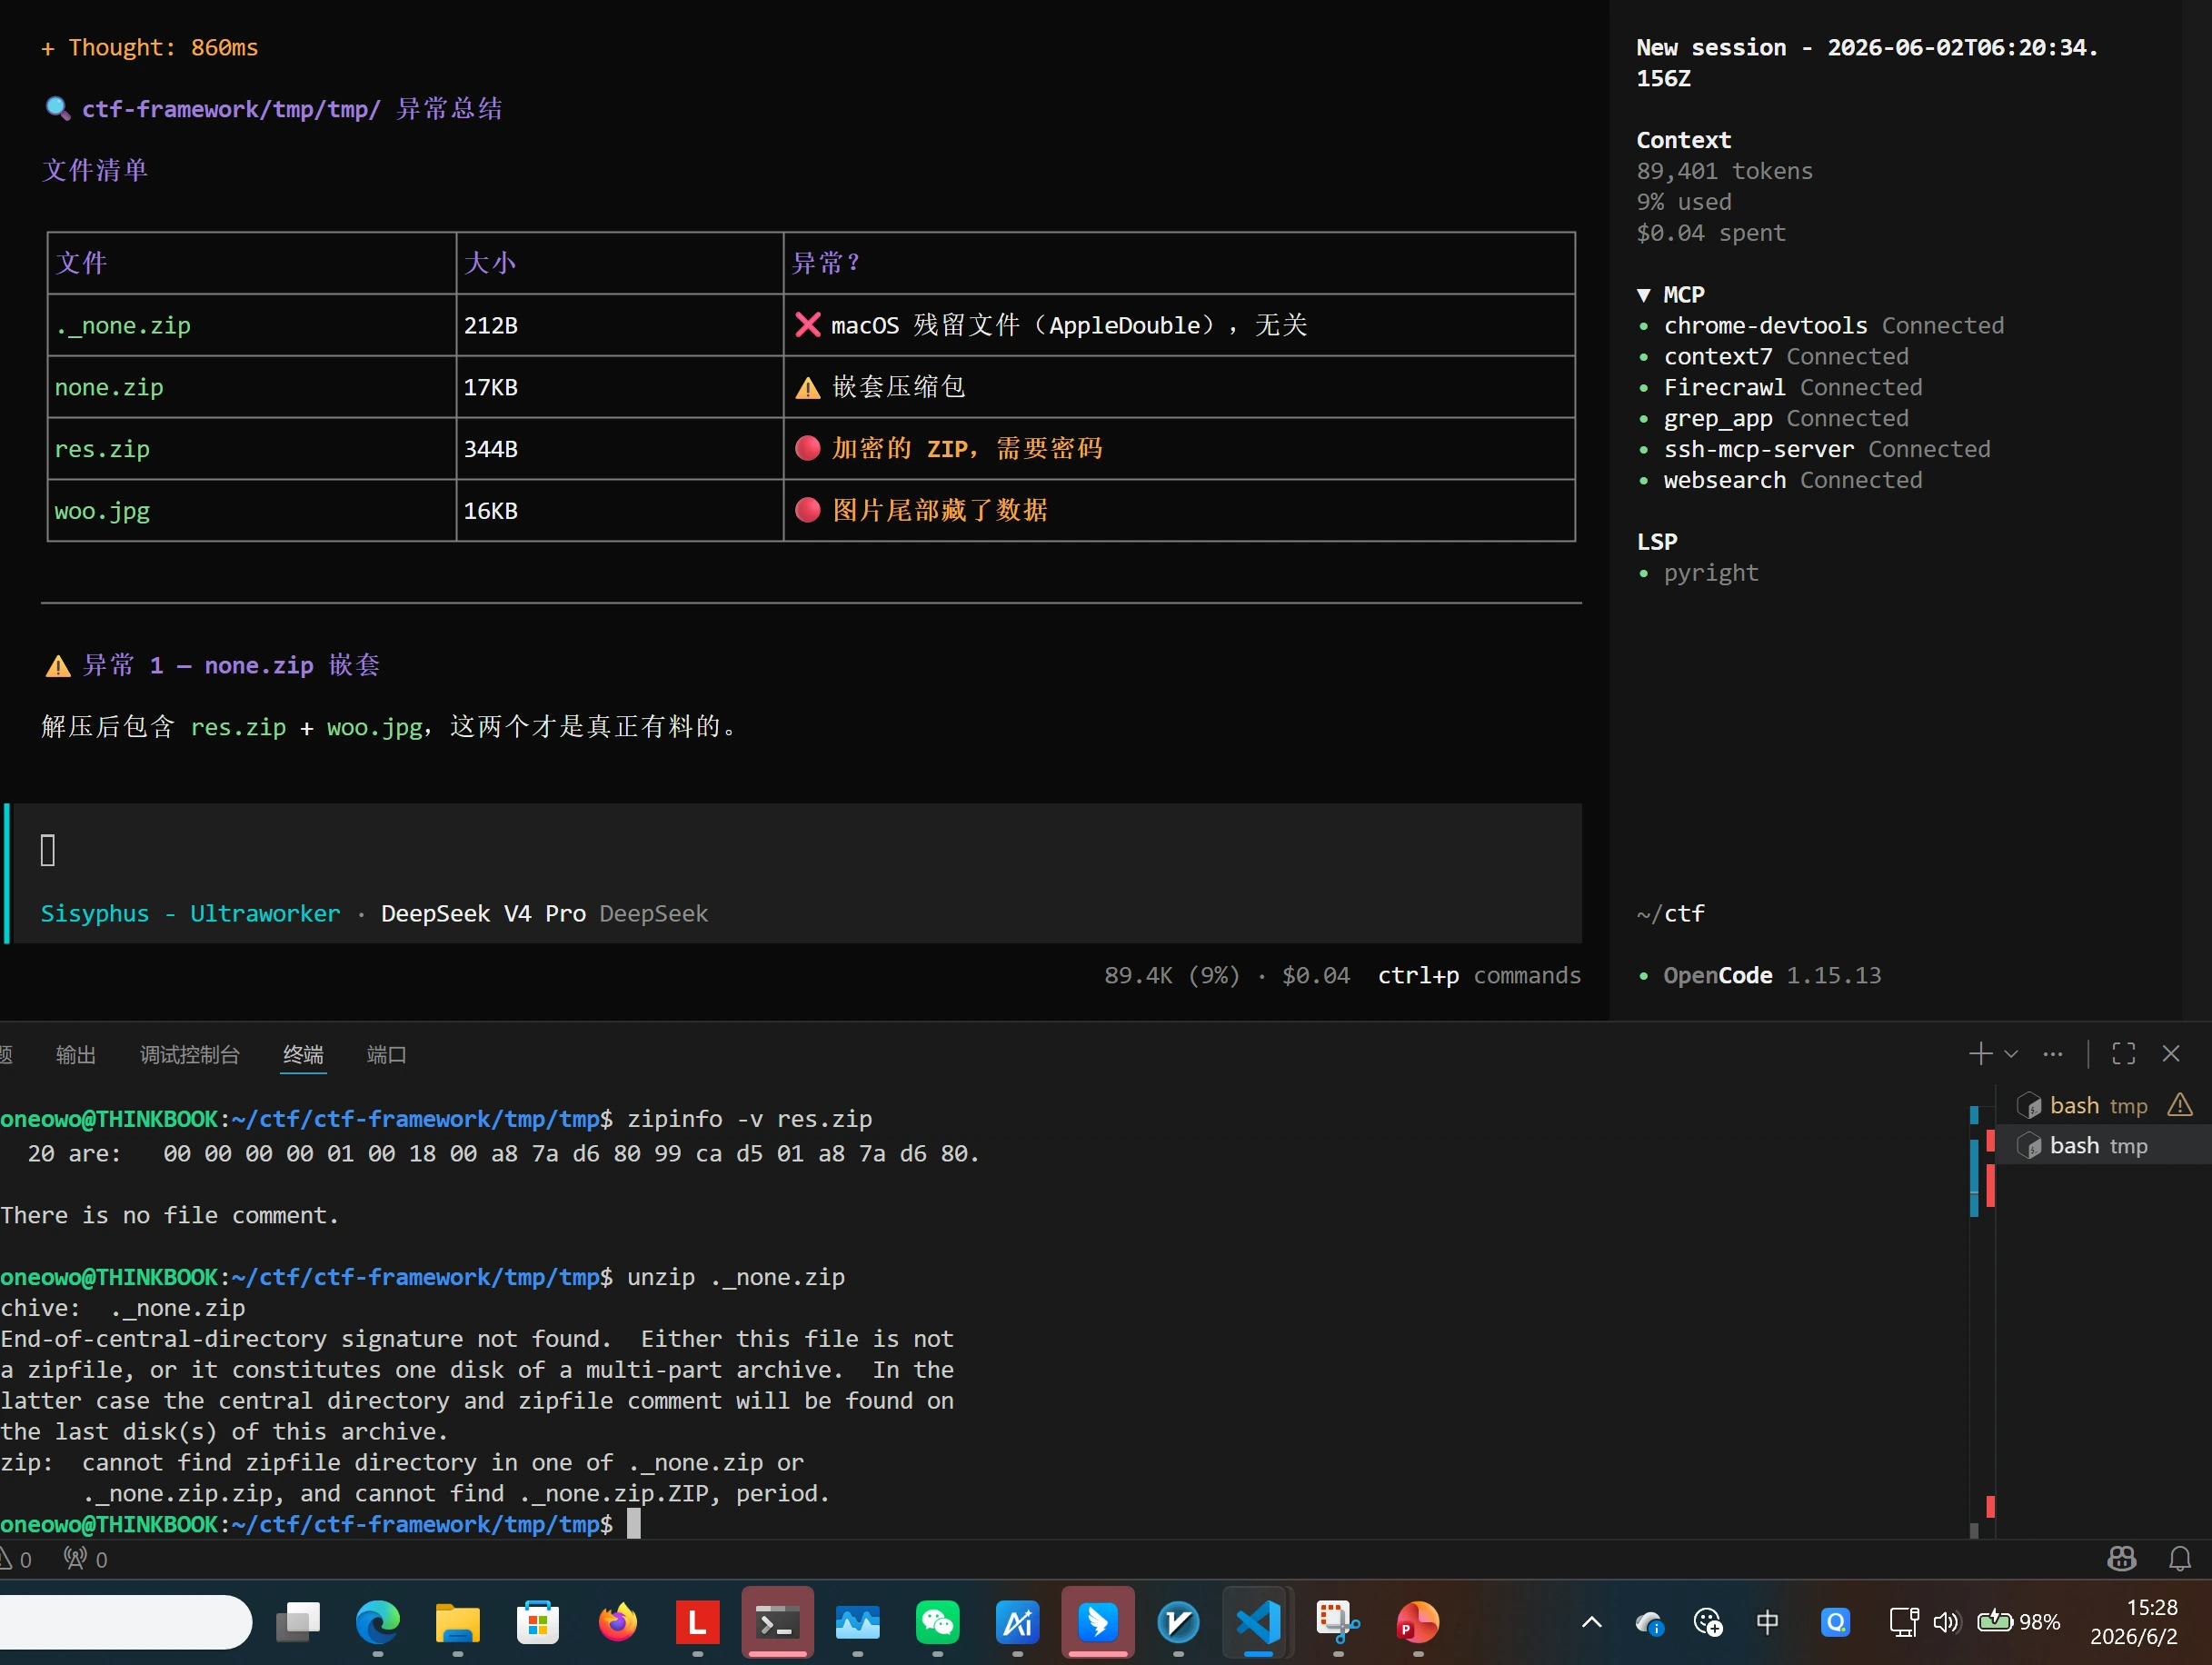 估计这个res的密码和这个图片有关系。让ai分析了一下图片
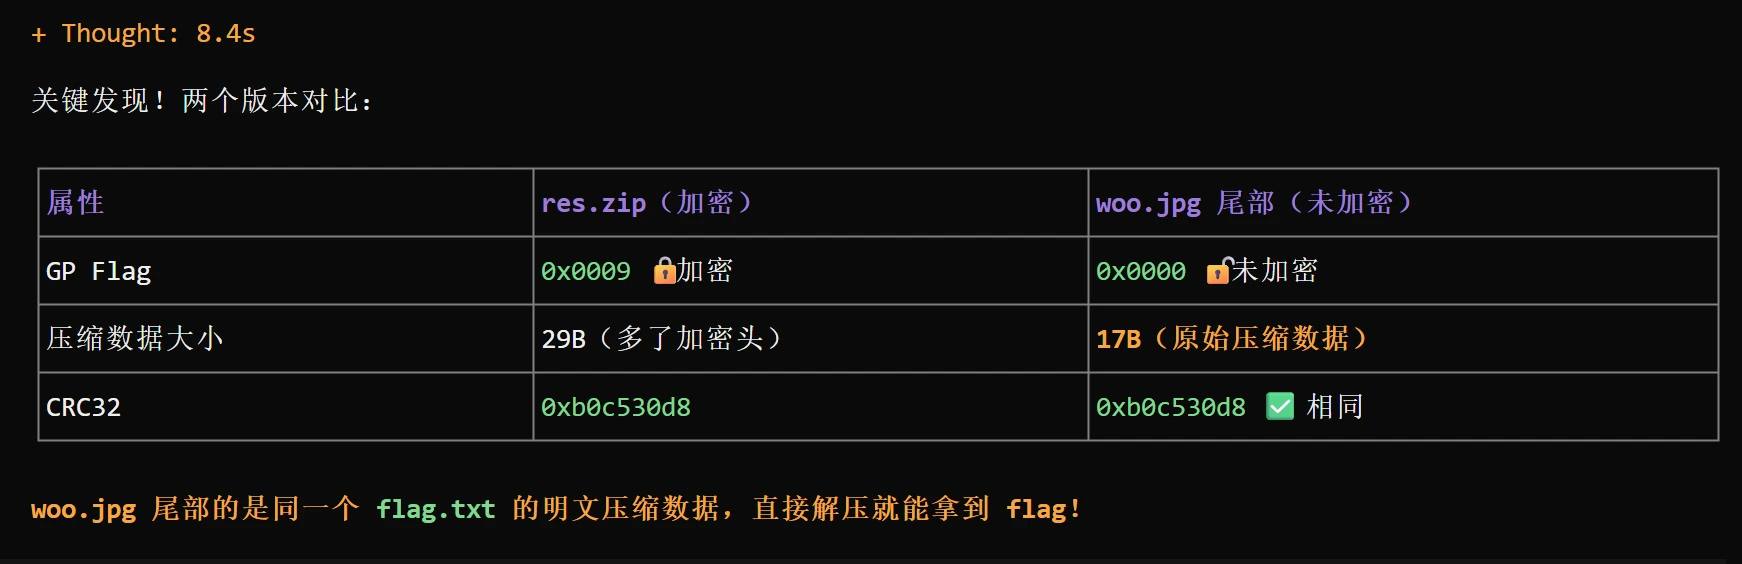 直接拿到flag,估计前面那个res是幌子this is the flag
指尖残影
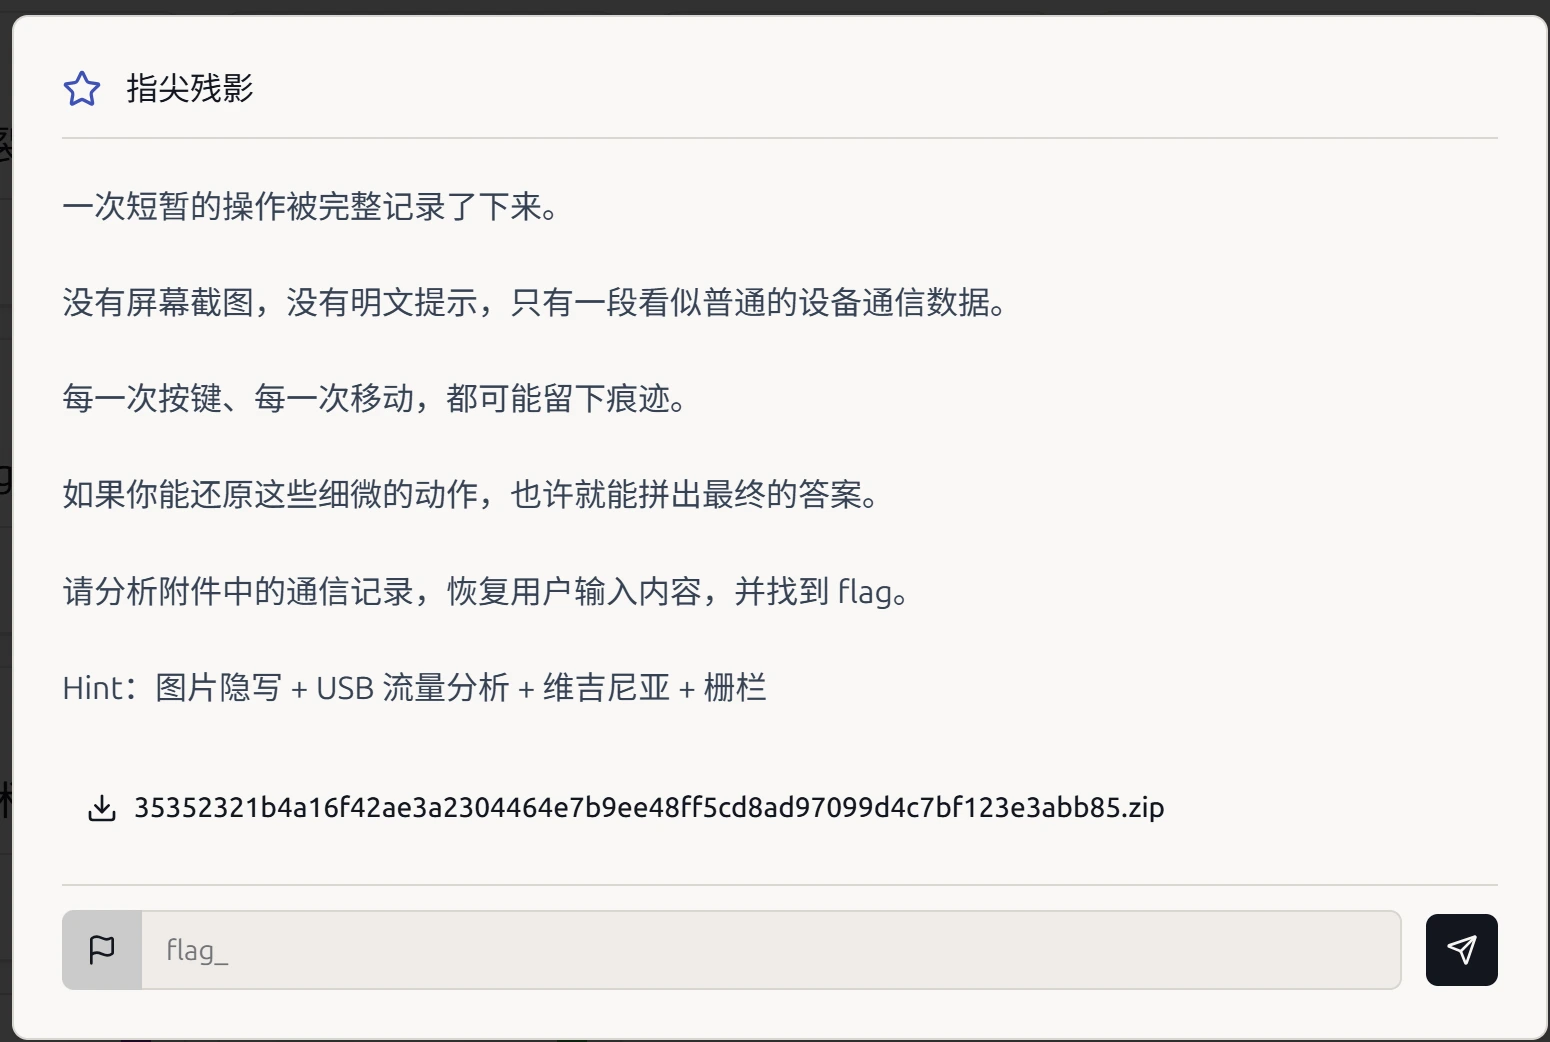 先把文件解压得到2个文件
1
2
3
4
| aloneowo@THINKBOOK:~/ctf/ctf-framework/tmp$ unzip 35352321b4a16f42ae3a2304464e7b9ee48ff5cd8ad97099d4c7bf123e3abb85.zip
Archive: 35352321b4a16f42ae3a2304464e7b9ee48ff5cd8ad97099d4c7bf123e3abb85.zip
inflating: 233.rar
inflating: key.ftm
|
继续解压233.rar会发现文件损坏。
让ai看一下文件情况然后修一下
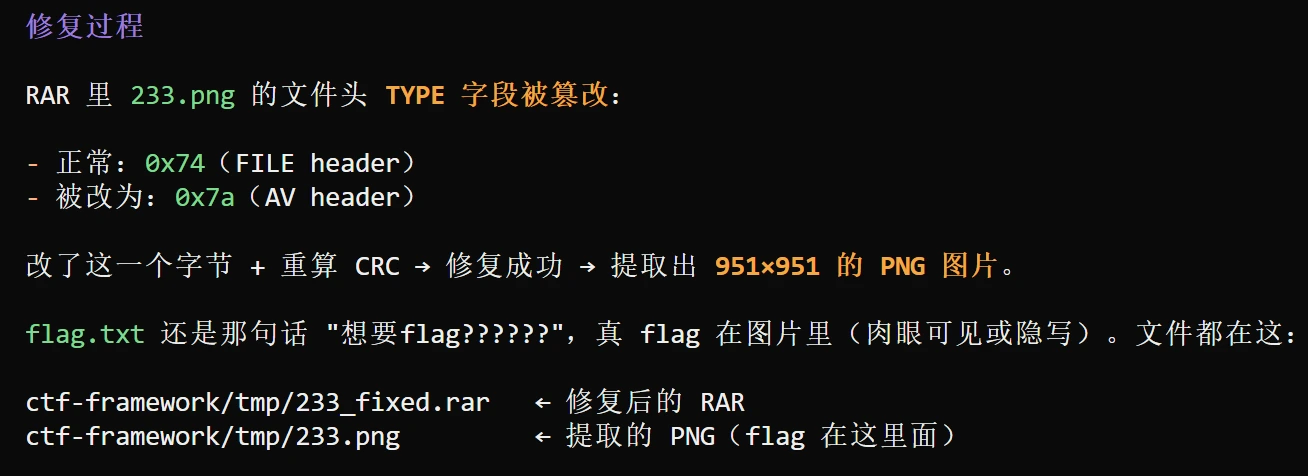 解压后看到了一个flag.txt还有一个png,那多半跟png有关
让ai处理一下图片